What Is Email Sandboxing?
Email sandboxing isolates malicious emails, allowing administrators to safely analyze them. Sandboxing prevents malicious emails from entering a user’s inbox and is an essential component of a unified security approach to protect against spear-phishing, evasive, emerging, and zero-day threats. An email sandbox provides an isolated test environment to check emails and prevent successful cyberattacks. If emails are deemed safe, they are automatically sent to the correct recipient.
How Does Email Sandboxing Work?
Email sandboxing analyzes suspicious emails and attachments in a secure, isolated environment before they reach the user. If a message, attachment, or embedded link appears suspicious, the system automatically isolates it for deeper inspection; a pre-filter step uses blocklists and antivirus to decide whether to detonate a suspicious email. The system will detonate a suspicious file in a controlled sandbox environment, where it can execute safely without risking the production network. During execution, the sandbox monitors the file’s behavior for signs of malicious activity such as unusual process execution, credential harvesting attempts, suspicious network connections, or attempts to download additional payloads.
Advanced behavioral analysis and machine learning evaluate the activity in real time to determine whether the file is safe or malicious. If malicious behavior is detected, the system blocks, quarantines, or deletes the threat before it reaches the user. If the email is verified as safe, it is automatically released to the recipient with minimal disruption to normal business operations. Advanced techniques like machine learning help ensure emerging and zero-day threats are detected.
Stop Unknown Threats Without Slowing Users or Margins
Email sandboxing plays an important role in layered email security. When combined with a secure email gateway (SEG), it helps MSPs stop malicious and unknown threats before they reach users without adding unnecessary operational complexity.
How Is Malware Delivered by Email?
Email is a favored method for delivering malware directly into an organization. Methods used to deliver malware via email include the following:
- Attachments - single-step process: an email containing an attachment is sent to an individual. The phishing attempt may target a specific individual, such as a system administrator, but it could target any employee. The attachment contains malicious code. If the attachment is opened, the malware contained within will install, i.e., the code will execute. If the code executes, it will install malware.
- Attachments - two-step process: a more sophisticated two-step attack is another variant of the infected attachment phishing email. In the two-step approach, the attachment contains code that downloads the final malware payload before auto-executing it on the device.
- Embedded links in attachments: Another strategy uses embedded links in an email message to direct users to an attacker-controlled website. If an employee clicks the malicious link, they are directed to a malicious site where they are tricked into downloading malware or divulging corporate network credentials. The malicious site typically spoofs a well-known brand. Hackers may have already gathered intelligence on the brands the target company uses. Because Microsoft 365 is popular, cyberattackers often spoof this brand to phish login credentials.
Some malware executables, once installed, are used to create backdoors for further malware attacks. This type of malware creates a “backdoor attack.” Backdoor malware can circumvent normal authentication measures, leaving the user’s machine open to remote control and allowing data eavesdropping software to run in the background of the machine. The malware-created backdoor lets cybercriminals steal data and install other malware, including ransomware, on the corporate network.
What Email Sandboxing Protects Against
Email sandboxing isolates suspicious emails and attachments in a secure environment for analysis before delivery.
This approach helps protect against:
- Spear phishing
- Zero-day malware
- Evasive threats
- Malicious attachments
- Emerging AI-assisted attacks
If an email is confirmed safe, it is released automatically. If it detects malicious behavior, it blocks the threat before it reaches the user.
Why Traditional Detection Misses Modern Threats
Traditional antivirus solutions rely heavily on signature-based detection, which works well against known threats but less well against new and evolving attacks.
Modern malware increasingly uses techniques such as:
- Fileless execution
- Polymorphic malware
- Metamorphic malware
- AI-assisted evasion
These threats continuously adapt to bypass conventional detection methods. As a result, MSPs need behavioral and execution-based analysis that can identify unknown threats in real time.
Benefits of Email Sandboxing
Email sandboxing as part of a broader email filtering solution offers several important benefits to an organization:
- Early detection of advanced attacks, prevention of data breaches, and reduced incident response costs and investigations.
- Ease of integration with your operating system environment using cloud implementations.
- Automatically stop threats before they execute in the business environment, including advanced persistent threats, targeted phishing attacks, malware evasion strategies, obfuscated executables, malware variants, customized malicious code, and ransomware.
- Continuous protection using artificial intelligence and machine learning against evolving advanced persistent threats.
- Cloud-based solutions make integrating an email sandbox into your email processes easy without making extensive changes to infrastructure configurations.
- Helps maintain compliance with the latest regulations and avoid hefty fines for violations.
How Sandboxing Reduces Risk for MSP Clients
Sandboxing gives MSPs an additional layer of protection against sophisticated email threats.
Suspicious emails can be:
- Held safely for inspection
- Executed in isolation
- Analyzed for malicious behavior
- Blocked or released automatically
This approach helps MSPs reduce exposure to emerging threats while demonstrating measurable security value to clients.
What MSPs Should Look for in a Sandboxing Solution
Not all email sandboxing solutions are designed for MSP environments. MSPs need protection that strengthens security without increasing operational complexity or reducing profitability.
When evaluating an email sandboxing solution, MSPs should look for:
- Protect against cyber-attacks: Early detection of advanced attacks, prevention of data breaches, and reducing incident response costs and investigations.
- Protect your network: Prevention of server and endpoint operating systems from being exposed to email-based threats.
- Easy to integrate and implement: Ease of integration with your operating system environment and email processes using cloud implementations.
- Stop advanced threats and leverage AI: Automatically stop threats before they execute in the business environment, including advanced persistent threats, targeted phishing attacks, and evasive malware. Continuous protection using artificial intelligence and machine learning against evolving advanced persistent threats.
- Cost-effective: Cost savings from removal of spam and other nuisance messages that exhaust storage capacity unnecessarily.
- Meet data regulations: Stay compliant with the latest regulations and avoid hefty fines for violations.
The right solution should help MSPs reduce alert fatigue, improve service efficiency, and deliver stronger client protection without adding unnecessary management overhead.
A vendor’s support model also matters. MSPs benefit most from partners that combine strong technical expertise, responsive support, and an MSP-first approach focused on long-term growth and customer success.
Sandboxing approaches explained
Types of Sandboxing: Inline vs Delayed
MSPs typically choose between inline and delayed sandboxing approaches.
- Inline sandboxing analyzes emails in real time before delivery using machine learning, static analysis, and behavioral detection. It offers fast, automated protection with minimal user disruption.
- Delayed sandboxing involves additional human review before release. While slower, it may be appropriate for higher-risk environments requiring extra scrutiny.
The right approach depends on client risk profile, operational requirements, and security priorities.
Deploying without slowing users
Effective sandboxing should strengthen security without reducing productivity.
Modern sandboxing solutions use AI-driven analysis and behavioral detection to process suspicious emails quickly and accurately. This helps MSPs maintain strong protection while minimizing delays to legitimate communications.
Balancing security, performance, and user experience is essential for successful deployment.
Reduces overhead?
Accuracy is critical to effective email sandboxing.
High false-positive rates create alert fatigue, increase support overhead, and delay legitimate email delivery. Poorly tuned detection can also block important business communications unnecessarily.
MSPs need sandboxing solutions that provide:
- Accurate threat analysis
- Clear workflows
- Flexible policy controls
- Easy tuning and management
Reducing operational friction helps MSPs improve service delivery while protecting client productivity.
Extending protection
Sandboxing works best as part of a unified security strategy that includes email filtering and security awareness training. Integrated protection across secure email gateways, XDR, endpoint security; threat intelligence improves visibility and strengthens detection across the entire attack surface.
Unified tools also simplify deployment and reduce management complexity for MSP teams.
Scaling across tenants
MSPs require sandboxing solutions designed for multi-tenant environments.
Scalable sandboxing platforms should provide:
- Centralized management
- Consistent policy deployment
- Secure tenant separation
- Rapid threat analysis
- Low administrative overhead
This enables MSPs to deliver enterprise-grade protection efficiently across their entire customer base.
Applying sandboxing where it matters
Not every client requires the same level of sandboxing. Granular policies and selective deployment help MSPs apply protection based on:
- Risk profile
- Industry requirements
- User behavior
- Compliance needs
Targeted deployment improves efficiency while ensuring protection focuses where it delivers the most value.
Improving margins with smarter protection
MSPs need security solutions that improve protection without increasing operational costs.
Integrated sandboxing within a unified email security platform helps reduce:
- Administrative overhead
- Tool sprawl
- Investigation time
- Support burden
This allows MSPs to improve operational efficiency while protecting profitability and delivering stronger client outcomes.
Proving protection
Sandboxing provides valuable threat intelligence that helps MSPs demonstrate security effectiveness.
Detonation reports reveal:
- Suspicious network activity
- File changes
- Process execution
- Malicious behaviors
These insights provide measurable evidence of protection while helping clients better understand their risk exposure.
Limitations of Email Sandboxing (and How to Mitigate Them)
Email sandboxes may have limitations unless they are designed to mitigate these known challenges:
- Complexity: Email sandboxes can be complex to configure and run, making them time-consuming and costly. Cybersentriq provides an integrated sandbox tool designed to be easy to use and cost-effective.
- Potential for sandbox evasion: Cybercriminals could build malware and phishing emails that evade detection. As cybercriminals become aware of email sandboxing, they may develop techniques to evade detection in a sandbox environment, for example, by detecting that a phishing email has been placed in a sandbox and changing its behavior to remain dormant in the sandbox but activate on a device. To help prevent this evasion tactic, Cybersentriq uses advanced intelligent technologies, such as AI, to predict and prevent advanced threats.
- Delays to legitimate email delivery: Sandboxing emails means that emails must be sent to a special area for testing before being released. This can delay some legitimate emails from reaching their intended audience. However, Cybersentriq’s multiple layers of security, coupled with our sophisticated sandbox technology, means we sandbox only specific, dangerous emails. Even if a legitimate email lands in a sandbox, delivery delays will be at most minutes.
- False positives: False positives are a concern for organizations implementing a sandbox. Organizations may be concerned that important emails could end up sandboxed. However, Cybersentriq quarantines emails before deletion, allowing an administrator to check their validity.
Email Sandboxing Best Practices
Choose a sandbox with multiple layers of defense
Email-borne threats are a challenge to conventional, signature-based antivirus. A sandbox is only as good as the detection mechanism used. Choose a solution that uses new-era AV software alongside behavioral analysis and machine learning to detect emerging, evasive, and zero-day threats.
Use a cloud-based, multi-tenant sandbox
An MSP needs an easily deployable, manageable sandbox to reduce administration overhead and costs. A cloud-based solution that integrates deeply into your tech stack and is multi-tenant by design gives MSPs the control to manage many clients from a single interface.
Configurable sandboxing on a per-organization basis
Each organization has its own threat levels and threat types. A sandbox must offer granular configurability to reflect these threats.
Monitor false negatives and false positives
A centralized console in a cloud-based sandboxing solution lets an MSP closely monitor quarantined emails and generate reports. This ensures false positives can be addressed swiftly to prevent delays in delivering legitimate emails. Reports can be used to fine-tune the sandbox settings to minimize false negatives.
Educating the workforce on email security
Security awareness training helps employees identify emails that evade the sandbox and report them promptly.
How CyberSentriq Email Sandboxing Works
Cybersentriq applies an aggressive pre-filter using Bitdefender Antivirus. This pre-filter determines if an email attachment should or should not be sent to the sandbox. If the engine recommends an attachment be sent to the sandbox, the following occurs:
- Cybersentriq uploads the attachment to the sandbox, where it is assigned a job identifier.
- Once in the sandbox, Cybersentriq queries the process every fifteen seconds (for up to twenty minutes) until the job is complete. During this period, the message delivery status in History is ‘Sent to Sandbox.’
- If no result is returned after twenty minutes, the file is marked as clean, and the email is sent on to the recipient.
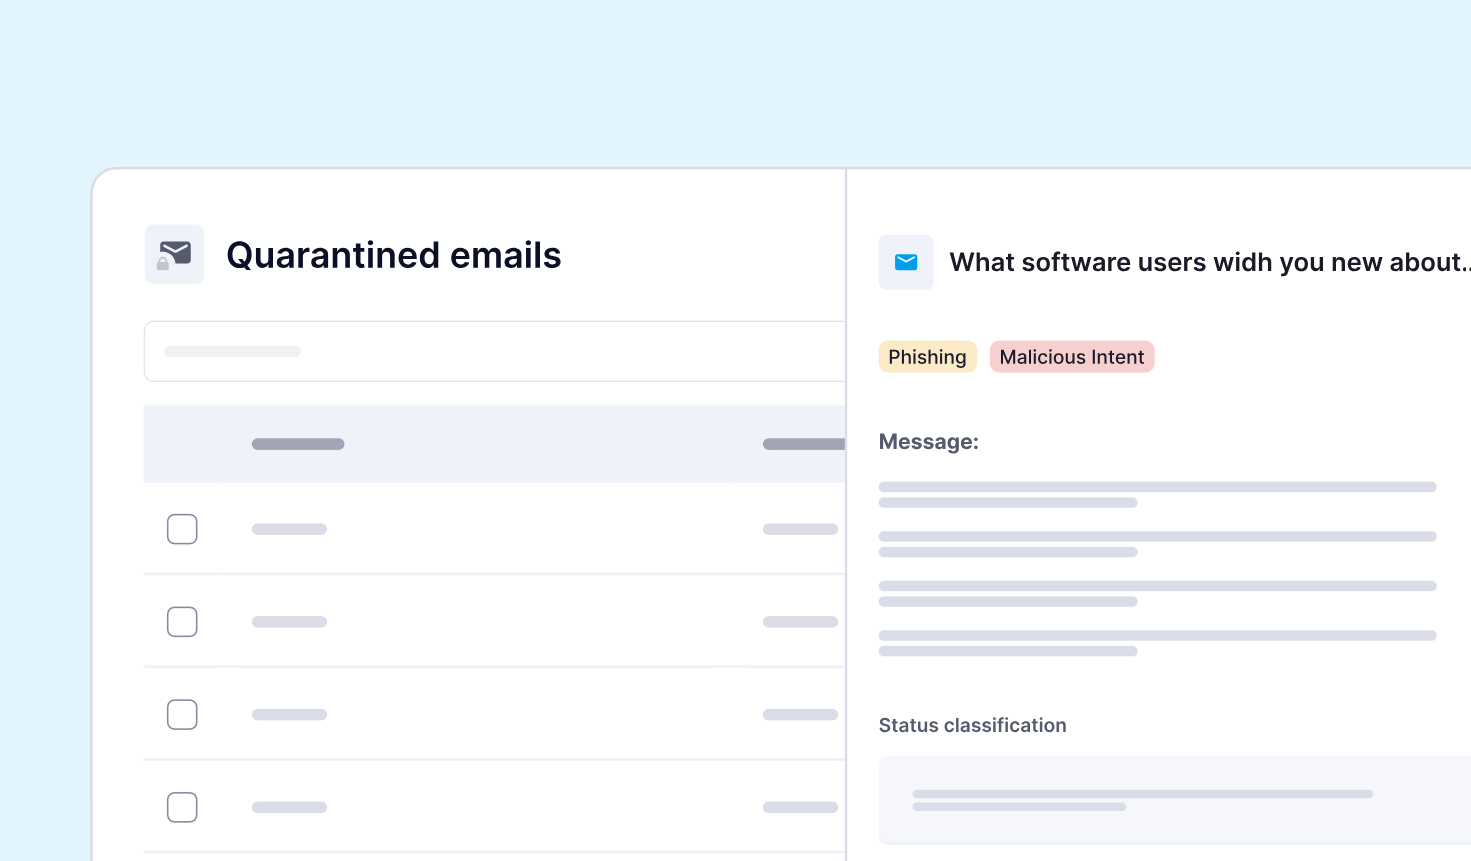
- If the sandbox identifies malware, the email is blocked as a virus with the virus name assigned as ‘ATP.Sandbox’. The message will be listed under ‘Viruses’ in the relevant Quarantine report.
- Sandboxed emails can be found in History. Go to Reporting > History > Mail Filters and check ‘Sandboxed.’
If a message blocked as spam is released and originally marked as ‘Sent to Sandbox’, Cybersentriq will re-scan the message against the Bitdefender Antivirus engine upon release. This may result in the message being blocked or sent to the sandbox.
How CyberSentriq Helps MSPs Scale Email Security
MSPs need a partner that understands operational reality, customer expectations, and scalable service delivery.
The right vendor combines:
- Strong technical expertise
- Responsive support
- Multi-tenant simplicity
- Scalable protection
- A true partner mindset
MSPs do not need more fragmented tools or reactive workflows. They need integrated protection that reduces operational burden, strengthens client trust, and scales profitably across every tenant.
At CyberSentriq, we help MSPs deliver layered email security that protects clients, reduces operational burden, and supports long-term growth.
Discover how CyberSentriq helps MSPs stop advanced email threats, reduce operational overhead, and scale protection across every client environment.
Email Sandboxing FAQs
Email sandboxing isolates suspicious emails and attachments in a secure environment to determine whether they are malicious before they reach the user.
Sandboxing safely executes suspicious files in an isolated environment so analysts can examine their behavior for malicious activity before delivery or blocking.
Yes. Sandboxing helps detect zero-day threats by analyzing file behavior rather than relying solely on known malware signatures.
Modern sandboxing solutions are designed to analyze suspicious emails quickly, minimising delays to legitimate email delivery.
Traditional antivirus detects known threats using signatures, while sandboxing analyses suspicious files and behaviour to identify unknown or emerging threats.
Yes. Native Microsoft 365 protections help stop common threats, but advanced sandboxing adds deeper analysis and protection against evasive, emerging, and zero-day attacks.
The message ‘queued for sandbox’ means the mail security system temporarily delays a message to perform deeper analysis by scanning attachments or links for malware. This is most likely because the email includes an attachment the system has flagged as risky, even though it passed the initial antivirus scans. Checks include safety and behavioral analysis and are performed inside a secure, isolated test environment (the sandbox).