Give customers a controlled path back after ransomware
Matthew Miller
Product Marketing Manager

Trusted by 3,000+ MSPs worldwide
The challenge
Prepare the copies, decisions and validation steps before an incident.
The problem
Ransomware interrupts work and creates doubt about which protected data can be restored safely and in what order.
Why it happens
Production data may be affected, compromise may predate encryption, and credentials or dependencies needed for recovery may also be disrupted.
If it stays unresolved
The customer stays offline longer while responders investigate recovery points, technicians can restore the wrong scope, and business owners lack a reliable view of progress.
How the products help
Microsoft 365 Backup offers independent off-site, immutable protected copies, including dual-copy protection for supported cloud data, and malware detection within backup data as an input to recovery-point assessment. Machines Backup provides supported machine recovery routes; Azure VM Backup adds protected copies and file-level or full VM recovery for supported Azure workloads. InstantData can help users access eligible priority files while broader restoration continues. Unified Email Security and DNS Security reduce relevant exposure before an incident; Entra ID Backup addresses supported identity changes. The MSP still coordinates containment, authorization, point selection and validation with the incident owner.
Make recovery point selection an incident decision
The fastest available restore can be the wrong restore if compromise began before encryption. The MSP and incident owner need to assess the point, target and conditions for resuming service. Malware signals in supported backup data can inform that assessment, alongside investigation and validation; they cannot prove that every retained copy is clean. Agree who authorizes the decision before an incident, and rehearse how the team reaches backup data if production credentials are affected.
Report recovery as a sequence of business milestones: access to the first priority files, restoration of the workload and confirmation that users can safely work. This gives technicians a clearer order of operations and gives the customer a more honest progress report. A rehearsed plan also exposes missing permissions and dependencies. Backup is the recovery layer within the incident process, while containment and assessment remain essential responsibilities.
Maintain recovery options beyond production data
For supported Microsoft 365 data, independent off-site storage and immutability help preserve a recovery option when production information is affected. Confirm the relevant protection, retention and administrative controls for each customer workload. For machine data, use the storage and recovery properties verified for that specific service.
Email Protection Built for MSPs
of spam, malware and malicious email blocked before it reaches the inbox
MSPs worldwide trust CyberSentriq to protect their customers
each user receives a unique, randomised phishing simulation
of cybersecurity expertise behind the CyberSentriq platform
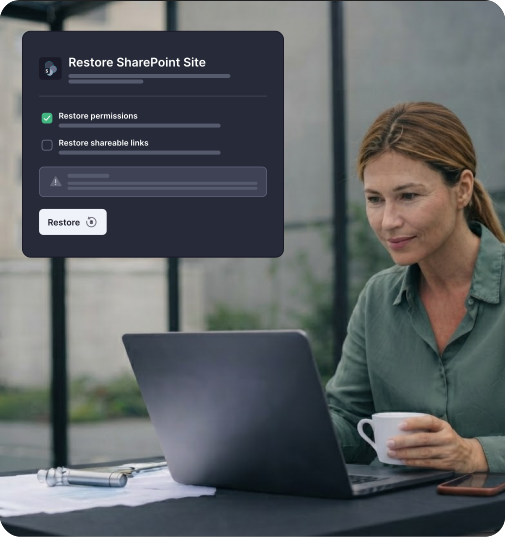
Choose a recovery point deliberately
The most recent copy is not always the right one to restore. CyberSentriq's Microsoft 365 and Azure VM backup capabilities include malware detection within backup data as an additional input for their supported workloads. Combine available evidence with the incident investigation, assess the potential point of compromise and authorize restoration into an appropriate environment.
Restore priority work and verify the result
Use granular restore and InstantData where supported to regain access to the information needed first. Track initial file access, restoration of the relevant workload and full business recovery as separate milestones. The MSP and incident owner validate that the threat is contained, the restored service works and users can safely resume operations.
A staged recovery in practice
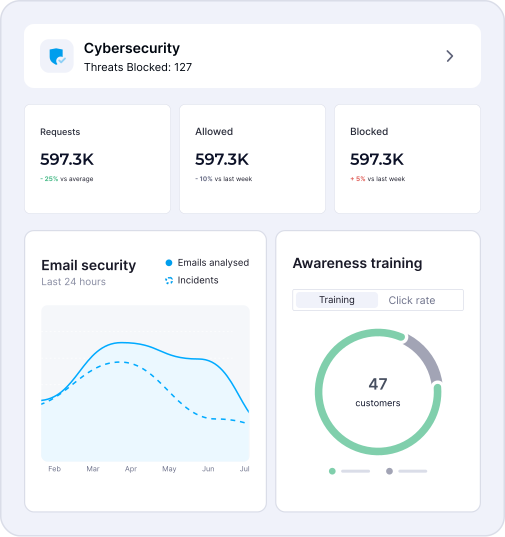
After a ransomware incident, the response owner confirms the conditions for restoration. The MSP reviews protected versions and available malware signals, chooses an appropriate recovery point with the incident team and restores a priority workload into a suitable environment. Users validate access and the business task before the MSP expands the restore. The decision record and milestones show progress from first usable data to restored workload and validated service. Backup supports this process; it does not contain the attacker or undo data exfiltration.