Help technicians act on the findings that matter
Matthew Miller
Product Marketing Manager

Trusted by 3,000+ MSPs worldwide
The challenge
Make the next technician action clearer and easier to account for
The problem
Technicians face findings spread across products and must work out what matters, what happened and which action belongs to them.
Why it happens
Separate workflows create context switching, while an unexplained risk score or automated action leaves too much interpretation to the service team.
If it stays unresolved
Investigation and customer explanations vary by technician, routine decisions consume specialist time, and the MSP has a harder time showing the value of its service.
How the products help
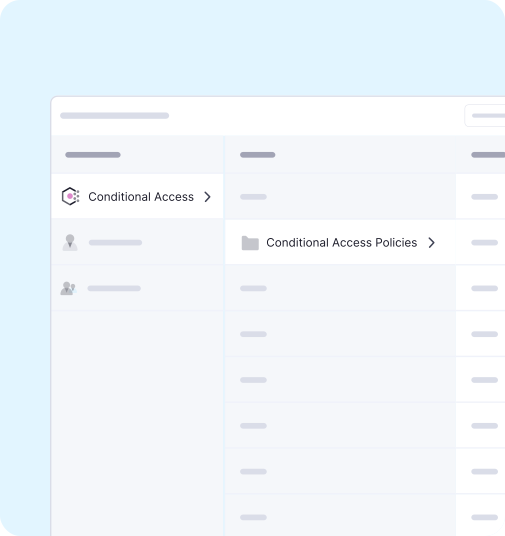
Sentriq provides the common operational experience, with Cyber Manager switching between security and data protection views. Within Unified Email Security, frontline checks and inbox-level monitoring feed a response that includes SentriqAI explainable verdicts, AI-assisted investigation and supported post-delivery remediation. Defined phishing quarantine can act automatically; backup restore is a separate named automation. The shared identity layer, API and supported partner integrations help the MSP design a consistent workflow.
Make each automated action accountable
An MSP does not gain much from another automated score if technicians still have to guess what it means. The useful unit of work is a finding with evidence, a defined action and a clear owner for the next decision. In email security, SentriqAI can explain a verdict and assist investigation; phishing quarantine can execute a defined action. A policy recommendation still needs technician review. Backup restore follows its own authorization and recovery process.
Turn those boundaries into an operating standard across customer accounts. Decide which events need human review, who can change a policy, when the customer must approve a consequential step and how completion is recorded. Cyber Manager helps the technician move between adopted product views, while the service procedure supplies accountability. The outcome for the customer is an explanation of what happened and what comes next, rather than an unexplained alert or a promise that every product acted automatically.
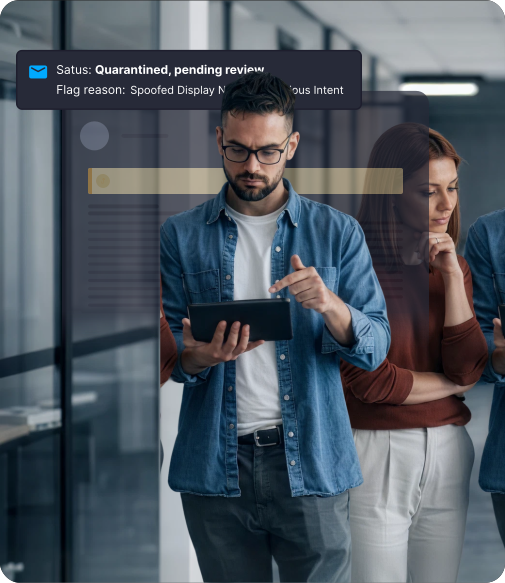
Understand the evidence behind an email finding
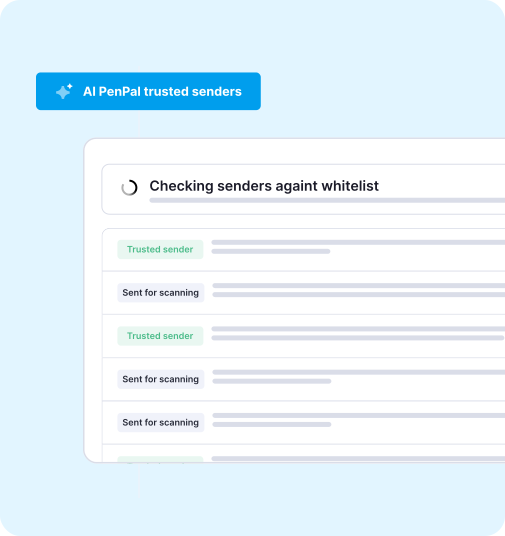
SentriqAI assesses message content, sender and authentication signals, links, intent and historical patterns to produce an explainable verdict. Instead of treating a risk score as the whole answer, your team can review the supporting signals and decide what investigation or customer response is needed.
Email Protection Built for MSPs
of spam, malware and malicious email blocked before it reaches the inbox
MSPs worldwide trust CyberSentriq to protect their customers
each user receives a unique, randomised phishing simulation
of cybersecurity expertise behind the CyberSentriq platform
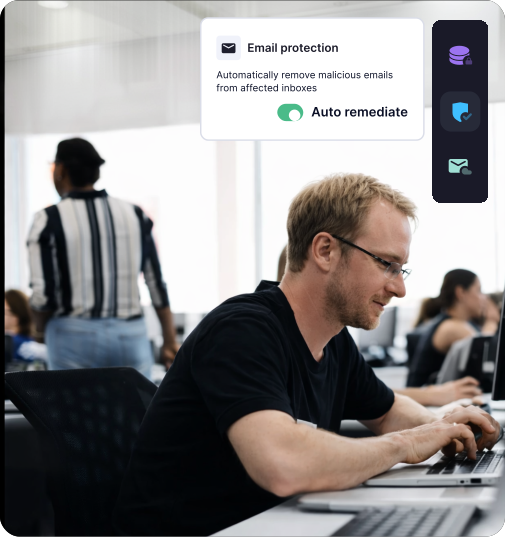
Know where automation acts and where your team decides
The platform distinguishes AI-assisted investigation and policy recommendations from named autonomous actions such as phishing quarantine and backup restore. Build that distinction into your service: define what happens automatically, what a technician reviews and which actions require customer approval or escalation. Customers gain a clearer explanation of both the decision and the person accountable for it.
Bring the workflow into service delivery
Cyber Manager lets technicians switch between security and data protection views in one click. A shared identity layer supports single sign-on and MSP identity-provider federation. The platform's common UI, API and data layer provide a foundation for a more consistent service, while partner and PSA integration options can be mapped to the way your team provisions services, manages cases and reports to customers.
SentriqAI's current intelligence is in email security. The shared data layer creates a path for future intelligence across the platform, including data protection and identity, as those capabilities become available.
A suspicious message in practice
A technician opens a customer email finding and reviews the signals that contributed to its verdict. If the message was quarantined, the technician can explain why; if a policy change is recommended, the technician evaluates it before applying it. The resulting customer update states the observed risk, the action already taken and any next step the customer owns. The MSP can carry that explanation into its customer review while using Cyber Manager to access other adopted product views as needed.